Mains Ready By December. Smash Mains & Smash PYQ Admissions Open

GS Paper: GS3-21.Role of External State and Non-state Actors in creating challenges to Internal Security.

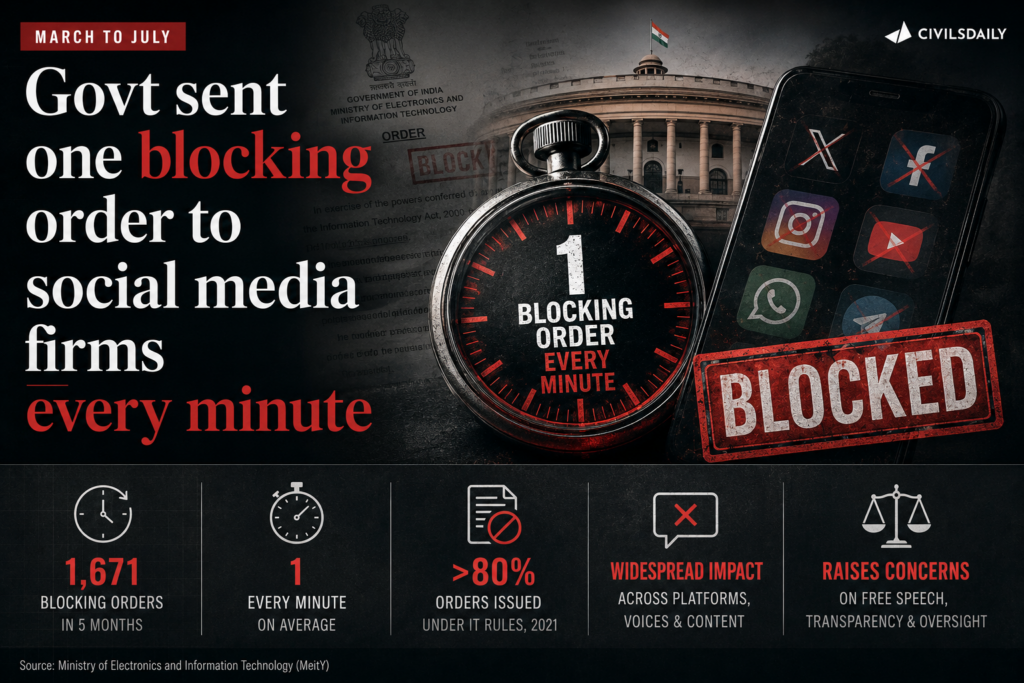
  • March to July, Govt sent one blocking order to social media firms every minute

    Why in the News

    Nearly 1.95 lakh state backed content blocking orders were sent to Instagram, Facebook and YouTube between March and July 2026, an average of one every 68 seconds, against a daily average of six in the preceding year. Most were routed through the Sahyog portal of the Ministry of Home Affairs and issued under Section 79(3)(b) of the Information Technology Act, 2000, the safe harbour condition, rather than the dedicated blocking power in Section 69A. The surge, combined with automated execution by the platform, converts a conditional legal duty into unconditional compliance.

    What is the Sahyog portal?

    1. What it is: A platform built by the Ministry of Home Affairs through which central and State agencies send content blocking notices to online intermediaries.
    2. Who uses it: Various central and State law enforcement and government agencies issue notices, and all three major social media companies have joined the portal.
    3. Legal hook: Notices are issued under Section 79(3)(b) of the Information Technology Act, 2000, the provision that conditions an intermediary’s legal immunity.
    4. What it replaced: It centralises what were previously scattered notices from individual police units and departments into a single automated channel.
    5. Scale of use: Between October 2024 and October 2025 the portal carried 2,312 blocking orders to 19 online platforms, a daily average of six.
    6. What one order covers: A single blocking order can cover hundreds of individual pieces of content or accounts, so the order count understates the volume removed.

    What is safe harbour under Section 79 of the Information Technology Act, 2000?

    1. The immunity: Section 79 protects an intermediary from liability for content that its users post, provided it does not initiate, select or modify that content.
    2. The condition: Section 79(3)(b) withdraws that immunity if the intermediary fails to remove unlawful material after receiving actual knowledge or a government notification.

    What is Section 69A of the Information Technology Act, 2000?

    1. The power: It allows the Union government to direct the blocking of public access to information in the interest of sovereignty, defence, security of the State, friendly relations, public order or the prevention of a cognisable offence.
    2. The safeguards: Blocking under it follows the Information Technology (Procedure and Safeguards for Blocking for Access of Information by Public) Rules, 2009, which require a committee review and reasons in writing.

    What is actual knowledge in intermediary liability?

    1. The test: Actual knowledge is the point at which an intermediary is informed of specific unlawful content and becomes obliged to act on it.
    2. Where it comes from: The Supreme Court in Shreya Singhal v. Union of India (2015) read down Section 79(3)(b) so that actual knowledge means a court order or a government notification, not a private complaint.

    What is an Application Programming Interface?

    1. What it is: A defined interface that allows one software system to send instructions directly to another without a person operating either end.
    2. Its use here: Meta has integrated its interface with the Sahyog portal, so a flagged item uploaded to the portal is removed from its platforms automatically.

    What does the scale of the blocking orders show?

    1. Total volume: Nearly 1.95 lakh blocking orders in five months, about 1,275 a day, or one every 68 seconds.
    2. Instagram: Around 1,00,000 orders, just over half of the total, and the platform on which the student protests were most visible.
    3. Facebook: Around 80,000 orders.
    4. YouTube: Nearly 15,000 orders.
    5. Concentration: Meta owned platforms received roughly nine out of every ten orders issued to the three companies.
    6. The baseline: The comparable figure for October 2024 to October 2025 was 2,312 orders across 19 platforms, a daily average of six.
    7. Official record: The Ministry of Home Affairs annual report for 2024 and 2025 recorded a little over 1.11 lakh pieces of suspicious online content blocked until March 2025 under Section 79(3)(b).
    8. Comparative removals: Meta reported removing over 23 million pieces of content in Indonesia between July and December 2025 against about 41,000 in India, which had already doubled from 28,000 in the first half of that year.
    9. User base: India has over 600 million social media users, with an estimated 10 million to 100 million posts a day.

    What changed in February 2026?

    1. The amendment: The Ministry of Electronics and Information Technology notified amendments to the Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules, 2021.
    2. The new deadline: Content must now be removed within two to three hours, against the earlier window of 24 to 36 hours.
    3. Added conditions: The amended rule requires that an order come from an officer of a prescribed rank and state its reasons.
    4. The compliance effect: A window of two to three hours makes case by case human review commercially impossible at Indian volumes.
    5. The platform response: Meta integrated its interface with the Sahyog portal so removal happens machine to machine, without separate human review.
    6. What was removed: Automation eliminates the room for the company to review or contest a directive before complying with it.

    Why does the shift from Section 69A to Section 79(3)(b) matter?

    1. Different purpose: Section 69A is a dedicated blocking power. Section 79(3)(b) is a condition attached to an immunity, not a power to censor.
    2. Different safeguards: Section 69A orders pass through a review committee under the 2009 Rules and carry recorded reasons. Section 79(3)(b) notices carry no equivalent statutory committee.
    3. Different issuing authority: Section 69A is exercised by the Union government. Section 79(3)(b) notices come from a wide range of central and State agencies through the portal.
    4. Different subject matter: Section 69A is largely confined to national security and public order. The portal route is used for a far wider category of content.
    5. The legal consequence: The intermediary that refuses a Section 79(3)(b) notice does not face a penalty. It loses immunity for all user content, which is a far larger risk.
    6. What that produces: The threat of losing safe harbour makes refusal irrational, so the conditional structure operates as a command.

    What content was targeted?

    1. The protest period: The five month window covered the student protests against examination paper leaks at Jantar Mantar in Delhi, which began in early June and were called off on 25 July after the resignation of the Union Education Minister.
    2. Official acknowledgement: A senior government official stated that a considerable share of the orders were issued as the protests gathered momentum, particularly on Instagram.
    3. Protest content: Users reported the removal of posts supporting the student protests.
    4. Policy criticism: Posts criticising the government’s ethanol fuel blending policy were among those blocked.
    5. Electoral content: Content relating to the West Bengal Assembly elections was also removed.
    6. Synthetic media: Deepfakes formed a further category among the removals.
    7. Political speech: The national convenor of a national political party stated that some of his Instagram posts were blocked in India.

    Where does automated compliance turn against the legal design?

    1. The doctrinal problem: Actual knowledge requires that someone at the company know of the content and assess the order. An interface that executes takedowns automatically has no knowledge at all.
    2. No verification of authority: Nobody at the company checks whether the order comes from an officer of the prescribed rank or states the reasons the amended rule requires.
    3. Conditional becomes unconditional: Machine to machine execution converts a conditional legal duty into unconditional compliance, which is the substance of the objection raised by the Internet Freedom Foundation.
    4. The state interest on the other side: Coordinated disinformation, deepfakes and incitement travel faster than any human review cycle, which is the case for a short deadline.
    5. The unequal risk: The cost of over removal falls on the user, who has no notice and no appeal. The cost of under removal falls on the company as loss of immunity for all content.
    6. Notice denied: Meta informs users which State authority sent a request in most markets, but not in India, citing legal obligations and regulatory considerations.
    7. No proportionality check: One order can cover hundreds of accounts, so a single instruction can remove speech at a scale no court has examined.

    Challenges to the content blocking regime

    1. Absence of a review committee: Orders under Section 79(3)(b) carry none of the committee scrutiny that Section 69A orders pass through. e.g. the 2009 Blocking Rules committee has no counterpart for portal notices.
    2. Secrecy of orders: Blocking directions are treated as confidential, so neither the user nor the public sees the reasoning. e.g. Rule 16 of the 2009 Blocking Rules requires confidentiality of complaints and actions taken.
    3. No pre decisional hearing for the user: The person whose speech is removed is not heard before removal and often not informed after it. e.g. account holders learning of removal only from the platform’s generic notification.
    4. Chilling effect on lawful speech: Platforms over comply to protect immunity, which removes lawful criticism along with unlawful content. e.g. removal of posts criticising the ethanol blending policy during the same five month window.
    5. Federal multiplication of issuers: A wide set of central and State agencies can issue notices, so there is no single accountable authority. e.g. the portal carried orders to 19 platforms from multiple agencies in the previous year.
    6. Litigation uncertainty: Platforms that challenge the portal route face the loss of immunity while the case runs. e.g. X Corporation’s challenge to the Sahyog portal before the Karnataka High Court, dismissed in 2025.
    7. Encryption and traceability conflict: The traceability requirement in the 2021 Rules cannot be met without weakening end to end encryption. e.g. the pending challenge by WhatsApp to Rule 4(2) of the 2021 Rules.
    8. Capacity asymmetry: Smaller Indian intermediaries cannot build automated compliance systems and face the same deadlines. e.g. the two to three hour removal window applies to every significant social media intermediary.

    Conclusion

    The volume of blocking orders has risen from six a day to about 1,275 a day, and the legal route has moved from a dedicated blocking power with statutory safeguards to a safe harbour condition that carries none. Automation completes the shift, because a system that removes content without any person reading the order cannot satisfy the actual knowledge standard the Supreme Court built the provision around. The amended rules are in force and the orders continue. The unresolved question is whether Section 79(3)(b) can lawfully function as a general censorship channel when the Constitution requires every restriction on speech to be traced to a specific ground and a recorded reason.

    “[2024, GS3, 15 marks] Social media and encrypting messaging services pose a serious security challenge. What measures have been adopted at various levels to address the security implications of social media? Also suggest any other remedies to address the problem.”
  • [7th August 2026] The Hindu OpED: Stop the scam: Digital arrest menace

    Why in the News

    The Supreme Court passed an order on 4 August 2026 on the digital arrest scam. It directed banks, states and regulators toward faster action on mule accounts and cyber fraud. The scams persist because they are run largely from overseas hubs.

    What is the digital arrest scam?

    1. Definition: Fraudsters impersonate authorities and coerce victims into transferring money under threat of fake arrest. There is no legal basis or process called digital arrest.
    2. Targets: Older victims fall prey through deference to authority and fear of legal trouble.
    3. New targets: Scammers now also target youth and professionals, and senior citizens whom advisories have not reached.

    Why are digital arrests keep happening?

    1. Human Psychology & Social Engineering: Cybercriminals use social engineering tactics to manipulate people into revealing sensitive information. Fraudsters also exploit emotions like fear (threatening legal action), excitement (fake lottery wins), or urgency (fake emergency fund requests). Cybercriminals often impersonate trusted sources such as banks, government agencies, or even close friends.
    2. Weak Cybersecurity Practices: Common weaknesses include weak password and credentials use, unpatched software and system and poor security hygiene.
    3. Rapidly Evolving Cybercrime Techniques: Cybercriminals constantly evolve their methods to stay ahead of security measures.
    4. Digital Payments & Financial Fraud Risks: With the rise of digital transactions, cybercriminals have developed sophisticated methods to exploit online payment systems like fake UPI requests & QR codes, card skimming & SIM swaps and crypto & investment scams.
    5. Dark Web & Cybercrime Networks: The dark web serves as a marketplace for stolen data, malware tools, and illegal activities. Cybercrime has become an organized industry where criminals buy and sell stolen data and identity theft, organised cyber-crime syndicates and also offer Ransomware-as-a-Service (RaaS) as well.
    6. Lack of Strong Cyber Laws & Enforcement: Despite increasing cyber threats, many scams go unpunished due to slow law enforcements response, cross border crime challenges and lack of cyber crime awareness and policies.

    What did the Supreme Court order?

    1. Debit holds: It directed the Reserve Bank of India (RBI) to circulate a standard operating procedure for temporary debit holds on mule accounts.
    2. State action: States must notify cybercrime coordination centres and operationalise electronic Zero FIRs.
    3. Compensation: An inter departmental committee must examine a victim compensation framework.
    4. Data cited: Complaints on the National Cyber Crime Reporting Portal fell from 1,23,672 in 2024 to 16,377 in the first half of 2026.
    5. Recovery: Money was restored in 36,290 cases involving Rs 18.05 crore.

    What are the key terms in the response?

    1. Indian Cybercrime Coordination Centre (I4C): the nodal body coordinating action against cyber fraud and running the reporting portal.
    2. Mule account: a bank account used to receive and move fraud proceeds across states.
    3. Zero FIR: a First Information Report that can be filed at any police station regardless of jurisdiction.
    4. MuleHunter.AI: a detection system used in over 20 banks to flag mule accounts.

    Why do these scams persist despite falling complaints?

    1. Nimble methods: Fraudsters route calls through SIM boxes to mask origin and appear as Indian numbers.
    2. Deepfakes: They deploy deepfakes on video calls to dupe victims and stay untraceable.
    3. Few convictions: Convictions are rare as many schemes are run from overseas scam compounds.
    4. Overseas hubs: Compounds operate in Myanmar, the wider Golden Triangle and Cambodia, some with official patronage.
    5. Trafficking link: Indians are trafficked and coerced to run digital crimes against fellow citizens.

    Conclusion

    Detection systems and swift account freezes limit the damage even when perpetrators escape conviction. The core problem lies in overseas scam compounds beyond domestic law enforcement reach. New Delhi must use diplomatic pressure with China, the United States and ASEAN to compel host countries to act.

    Back2Basics

    Electronic-Zero FIR (e-zero FIR)

    An e-Zero FIR is an automated digital system in India that converts high-value cyber financial fraud complaints (above ₹10 lakh) filed via the National Cyber Crime Reporting Portal or the 1930 helpline directly into a Zero FIR. It eliminates jurisdictional delays during the critical “golden hour” for fund recovery

    Key Features and Workflow

    1. Automatic Registration: Eligible financial fraud reports trigger an instant e-Zero FIR without requiring an initial physical station visit.
    2. System Integration: Combines the I4C portal, state e-FIR mechanisms, and the NCRB’s Crime and Criminal Tracking Network & Systems (CCTNS).
    3. Auto-Routing: The system instantly routes the electronic document to the correct territorial cybercrime station based on the victim’s location.
    4. Mandatory Follow-Up: Complainants must visit the designated local police station within three days to sign and convert the e-Zero FIR into a regular FIR under the Bharatiya Nagarik Suraksha Sanhita (BNSS).

    PYQ Relevance

    [UPSC 2022] What are the different elements of cyber security? Keeping in view the challenges in cyber security, examine the extent to which India has successfully developed a comprehensive National Cyber Security Strategy.

    Linkage: The PYQ tests India’s cyber security framework and response to cybercrime. The article highlights recent measures to strengthen India’s response to digital arrest scams and cyber fraud.

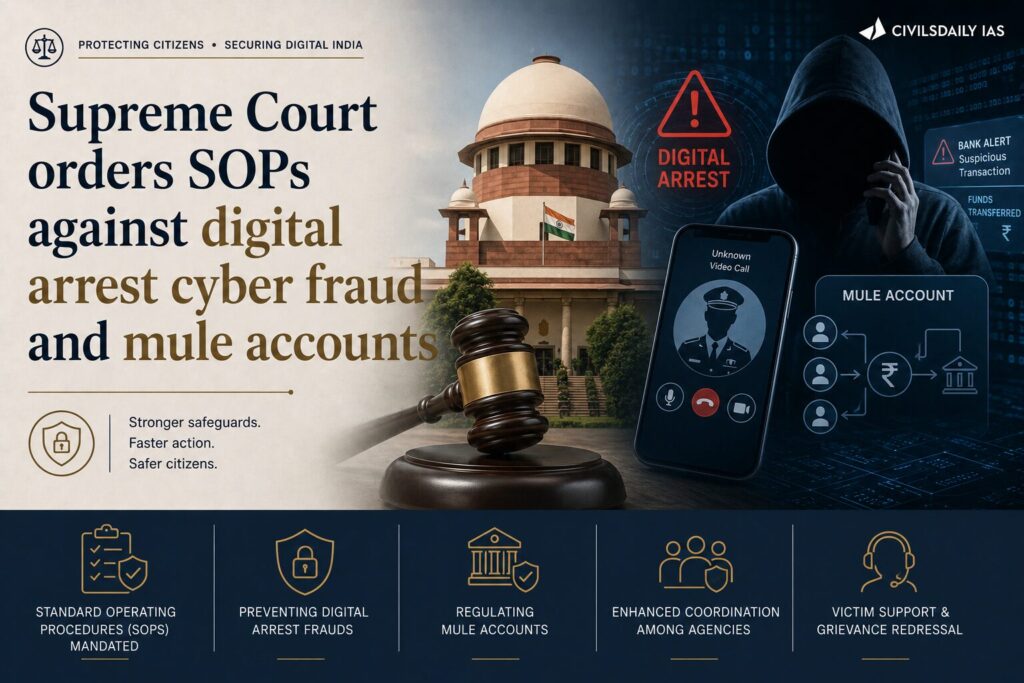
  • Supreme Court orders SOPs against digital arrest cyber fraud and mule accounts

    Why in the News

    The Supreme Court directed the Centre, States, and Union Territories to implement Standard Operating Procedures (SOPs) within four weeks to curb digital arrest cyber fraud, including freezing mule accounts, strengthening grievance redressal, and improving cybercrime coordination.

    What is a Digital Arrest Scam?

    • A cyber fraud where scammers impersonate police or enforcement agencies through video/audio calls.
    • Victims are falsely told they are under “digital arrest” and coerced into transferring money.

    What is a Mule Account?

    • A bank account used to receive and transfer proceeds of cyber fraud.
    • Often opened by unsuspecting or paid individuals.
    • Banks can impose temporary debit holds to prevent fraudulent withdrawals.

    What is the Indian Cyber Crime Coordination Centre (I4C)?

    • A nodal agency under the Ministry of Home Affairs (MHA) for coordinating India’s response to cybercrime.
    • Operates the National Cyber Crime Reporting Portal (NCRP) and the 1930 Cyber Helpline.

    Supreme Court Directions

    • Reserve Bank of India (RBI) to issue SOPs for temporary debit holds on mule accounts.
    • States/UTs to operationalise:
      • State Cyber Crime Coordination Centres.
      • e-Zero FIR mechanism.
    • Strengthen grievance redressal, money restoration, and public awareness.

    Challenges

    • Cross-border cybercrime networks.
    • Rapid movement of funds through mule accounts and cryptocurrencies.
    • Weak inter-agency coordination.
    • SIM spoofing and fake identities.
    • Low public awareness, especially among the elderly.

    Value Addition

    e-Zero FIR

    • Enables registration of a cybercrime complaint without jurisdictional barriers.
    • The complaint is later transferred to the appropriate police station.

    Citizen Response to Financial Cyber Fraud

    • Call 1930 immediately.
    • Report the incident on the National Cyber Crime Reporting Portal (NCRP).
    • Early reporting increases the chances of freezing fraudulent transactions.

    Back2Basics: Indian Cyber Crime Coordination Centre (I4C)

    • Parent Ministry: Ministry of Home Affairs (MHA).
    • Established: 2020.
    • Key Components:
      • National Cyber Crime Reporting Portal (NCRP).
      • 1930 Financial Cyber Fraud Helpline.
    • Mandate: Coordinate law enforcement, banks, telecom operators, and other stakeholders to prevent and investigate cybercrime.

    “[2017] In India, it is legally mandatory for which of the following to report on cyber security incidents?
    1. Service providers
    2. Data Centres
    3. Body corporate
    (a) 1 only
    (b) 1 and 2 only
    (c) 3 only
    (d) 1, 2 and 3

  • The legal patchwork facing doxxing victims in India

    Why in the News?

    The online targeting of women protesters has highlighted the absence of a dedicated law against doxxing in India, forcing victims to rely on scattered legal provisions.

    What is Doxxing?

    • Doxxing is the unauthorised public disclosure of a person’s private or personal information online to harass, intimidate or threaten them.
    • It can lead to stalking, identity theft, threats and physical harm.

    Existing Legal Framework

    • Bharatiya Nyaya Sanhita (BNS), 2023: Provisions relating to stalking, criminal intimidation and harassment.
    • Information Technology (IT) Act, 2000: Covers privacy violations and unauthorised disclosure of personal information.
    • Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules, 2021: Prescribe due diligence obligations for online platforms and provide safe harbour protection.

    Challenges

    • No specific offence for doxxing under Indian law.
    • Delays in content removal and prosecution.
    • Difficulty in fixing platform liability due to safe harbour provisions.
    • Rising digital threats to privacy and safety.

    Prelims Facts

    • The Digital Personal Data Protection (DPDP) Act, 2023 governs the processing of personal digital data but does not specifically criminalise doxxing.
    • Safe Harbour under Section 79 of the Information Technology (IT) Act, 2000 protects intermediaries from liability if they comply with due diligence requirements.

    [2024] Under which of the following Articles of the Constitution of India, has the Supreme Court of India placed the Right to Privacy?

    (a) Article 15

    (b) Article 16

    (c) Article 19

    (d) Article 21

  • Centre asks states to set up exclusive NDPS courts

    Why in the News?

    The Ministry of Home Affairs (MHA) has directed States and Union Territories to establish exclusive NDPS courts to tackle the backlog of nearly 39 lakh drug-related cases. However, 22 States are yet to comply.

    What is the NDPS Act?

    • The Narcotic Drugs and Psychotropic Substances (NDPS) Act, 1985 is India’s primary law to regulate and prohibit narcotic drugs and psychotropic substances.
    • The Narcotics Control Bureau (NCB) is the apex agency for enforcement.
    • The Narco-Coordination Centre (NCORD) coordinates anti-drug efforts among Central and State agencies.

    Why Exclusive NDPS Courts?

    • Speed up disposal of nearly 39 lakh pending cases.
    • Ensure specialised and faster trials for drug offences.
    • Improve conviction rates and reduce judicial delays.

    Significance

    • Strengthens deterrence against drug trafficking.
    • Helps curb crimes linked to money laundering, organised crime and terror financing.
    • Enhances India’s internal security, especially along vulnerable border regions.

    Challenges

    • 22 States have not yet established exclusive NDPS courts.
    • Need for adequate judges, prosecutors and infrastructure.
    • Court reforms must be complemented by effective enforcement and rehabilitation.

    Is it Mandatory?

    • Legally: The NDPS Act empowers State Governments to establish Special Courts, but it does not make exclusive NDPS courts mandatory in every district.
    • Administratively: The Ministry of Home Affairs (MHA) has strongly directed States and Union Territories to establish exclusive NDPS courts due to the huge backlog. While this directive is not directly enforceable like a statute, States are expected to comply in the interest of effective criminal justice and internal security.

    Prelims Facts

    • NCORD was established in 2016 to improve inter-agency coordination against drug trafficking.
    • NDPS Act, 1985 replaced the Opium Act, 1857, the Opium Act, 1878, and the Dangerous Drugs Act, 1930.
    • The NCB functions under the Ministry of Home Affairs (MHA).

    [2018, GS3, 15 marks] India’s proximity to two of the world’s biggest illicit opium-growing states has enhanced her internal security concerns. Explain the linkages between drug trafficking and other illicit activities such as gunrunning, money laundering and human trafficking. What counter-measures should be taken to prevent the same?”

  • India Becomes Free from Left Wing Extremism (LWE)

    Why in News?

    The Ministry of Home Affairs (MHA) announced that India became free from Left Wing Extremism (LWE) in March-April 2026, following sustained implementation of the National Policy and Action Plan (2015).

    Key Highlights

    • No district is currently categorized as LWE-affected.
    • LWE-affected districts reduced from: 126 (2014) → 90 (2018) → 70 (2021) → 38 (2024) → 8 (2025) → 0 (2026).
    • 37 districts are now classified as Legacy & Thrust Districts for continued security and development support.
    • 1 district remains a District of Concern for continued surveillance.

    National Policy and Action Plan (2015)

    • Adopts a Whole-of-Government Approach focusing on: Security operations. Infrastructure and connectivity. Welfare and development. Protection of tribal rights. Good governance and financial inclusion.

    Major Government Initiatives

    Security Measures

    • Security Related Expenditure (SRE) Scheme.
    • Modernisation of Police Forces (MPF).
    • Special Infrastructure Scheme (SIS).
    • Assistance to Central Agencies for LWE Management (ACALWEMS).
    • Surrender-cum-Rehabilitation Policy for Maoist cadres.

    Development Measures

    • 15,189 km roads constructed in LWE areas.
    • 9,497 telecom towers commissioned.
    • 179 Eklavya Model Residential Schools (EMRS) functional.
    • 47 ITIs and 49 Skill Development Centres established.
    • 6,025 post offices with banking services opened.
    • Security camps are being converted into Jan Suvidha Kendras.

    Other Initiatives

    • Special Central Assistance (SCA) for infrastructure.
    • Tribal Youth Exchange Programme (TYEP).
    • Civic Action Programme (CAP) to improve community engagement.
    • Distribution of over 21 lakh Forest Rights Act title deeds.

    [2023] Consider the following statements:
    1. According to the Constitution of India, the Central Government has a duty to protect States from internal disturbances.
    2. The Constitution of India exempts the States from providing legal counsel to a person being held for preventive detention.
    3. According to the Prevention of Terrorism Act, 2002, confession of the accused before the police cannot be used as evidence.
    How many of the above statements are correct?

    [A] Only one

    [B] Only two

    [C] All three

    [D] None

  • How Serious Is the Kudankulam Data Leak

    Why in the News?

    A ransomware breach at Yotta Data Services, a third-party data-centre vendor for Reliance Infrastructure Ltd, led to the leak of 14.3 GB of operational data related to the Kudankulam Nuclear Power Plant on the dark web platform World Leaks. Nuclear Power Corporation of India Limited (NPCIL) states the breach did not touch core reactor or nuclear-security systems, but the incident exposes how strategic nuclear infrastructure remains vulnerable through third-party digital supply chains.

    What exactly happened, and how did the breach occur?

    1. Breach reported: Reports emerged that multiple gigabytes of data on Kudankulam Nuclear Power Plant operations were copied and leaked as part of a ransomware attack.
    2. Point of infiltration: The infiltration targeted Reliance Anil Dhirubhai Ambani Group’s Reliance Infrastructure Ltd, not NPCIL directly.
    3. Scale of leak: 14.3 GB of Kudankulam-related data formed part of a larger 1.2 TB dataset hosted on World Leaks.
    4. World Leaks: World Leaks is a dark web site operated by cybercriminals who infect firms with ransomware and threaten to publish stolen data if a ransom is not paid.
    5. Trigger for publication: The site claims the ransom was not paid, resulting in the data being leaked publicly.

    Was the reactor or nuclear-safety systems compromised?

    1. NPCIL’s position: NPCIL states the leaked files pertain only to Balance of Plant (BOP: conventional common service facilities of a power plant, distinct from the reactor core) and not to nuclear safety or security-related systems.
    2. Reliance’s position: Reliance states no ransomware execution, data loss, or lateral movement occurred, despite confirming a partial breach of data hosted on Yotta’s servers.
    3. Nature of leaked files: The files reportedly include equipment blueprints, supplier details, meeting and inspection records, and equipment reviews.
    4. Insurance detail exposed: A $112 million insurance policy against terrorist attacks was among the leaked details, with the premium amount undisclosed.

    Why does the official reassurance not fully resolve the concern?

    1. Narrow definition of harm: Restricting concern to “core reactor systems” ignores that BOP data such as blueprints and inspection records can still aid reconnaissance or attack planning against a strategic facility.
    2. Layered outsourcing risk: Reliance itself depends on a third-party vendor, Yotta, for data hosting, showing that critical infrastructure security depends on vendors several steps removed from NPCIL.
    3. Self-assessment, not independent audit: Both Reliance and Yotta’s claims that no ransomware execution or lateral movement occurred rest on the vendor’s own internal forensic assessment, not an independent verification.
    4. Transparency gap: The premium amount for the $112 million terrorism insurance policy remains undisclosed even after the leak, showing incomplete disclosure despite the reassurances offered.

    What does the incident reveal about the plant’s strategic significance going forward?

    1. Current capacity: Kudankulam has commissioned two 1,000 MWe VVER (a Russian-designed pressurised water reactor type) units, supplying up to two gigawatts, built in partnership with Russian firm Rosatom.
    2. Expansion underway: The government plans four more units at the site, which would triple installed capacity, expanding the facility’s strategic value and its digital attack surface.
    3. Gap between messaging and internal concern: The revelations have caused “absolute commotion” among plant officials internally, even as public statements downplay the breach’s significance.

    Conclusion

    The Kudankulam leak shows that reassurances confined to “core reactor safety systems” do not address the full risk profile of a strategic nuclear facility. This is because non-core operational data hosted through layered third-party vendors remains commercially and strategically sensitive. As Kudankulam’s capacity is set to triple, critical infrastructure protection frameworks need to extend cybersecurity accountability across the entire vendor supply chain, not the reactor core alone. Additionally this requires independent verification rather than self-reported vendor assessments.

    PYQ Relevance

    [UPSC 2023] What are the different elements of cybersecurity? Keeping in view the challenges in cybersecurity, examine India’s preparedness in preventing cyber attacks.

    Linkage: The article highlights cybersecurity challenges in protecting India’s critical infrastructure from ransomware and third-party data breaches. The Kudankulam data leak underscores the need to strengthen cyber resilience, vendor security, and protection of critical infrastructure despite no compromise of reactor systems.

  • India’s eastern border affected by flow of opium from Myanmar

    Why in the News?

    The Narcotics Control Bureau (NCB) released its 2026 annual report on 27 June 2026, tabled by Home Minister Amit Shah. The report documents Myanmar’s emergence as the primary global opium source following the Taliban’s 2022 ban on drug cultivation in Afghanistan. Infact, India’s northeastern border corridor is identified as the most direct and porous entry point for this expanding production base. 

    What change in the global narcotics supply chain has created new pressure on India’s northeastern borders?

    1. Taliban-imposed ban: The Taliban government’s 2022 ban on drug cultivation in Afghanistan eliminated the world’s largest opium producer from the supply chain, creating a vacuum in global opium supply.
    2. Myanmar’s replacement role: Myanmar filled this vacuum rapidly. The NCB’s 2026 annual report identifies Myanmar as the alternative global opium source, with consequences already visible along India’s eastern borders.
    3. Scale of cultivation expansion: Myanmar’s illicit opium cultivation expanded by approximately 56% between 2021 and 2023. The area under poppy cultivation reached 45,200 hectares.
    4. Golden Triangle transformation: Myanmar’s Golden Triangle has expanded beyond its traditional opiate role. Shan State now produces both opium and methamphetamine (Yaba), making it a major poly-drug hub.
    5. Manipur corridor as primary entry point: National Highway-102 through Manipur is the main land route for heroin and methamphetamine into India.
    6. Secondary corridor via Mizoram: Champhai in Mizoram provides the second major trafficking route via Myanmar’s Chin State. Drugs are routed through Assam’s Barak Valley via Aizawl and adjoining road networks.

    How have India’s northeastern states been transformed from transit zones into active narcotics staging grounds?

    1. Porous border mechanisms: The Free Movement Regime (FMR) along the India-Myanmar border and unfenced border stretches have converted the Northeast from a transit route into a distribution hub.
    2. States bearing frontline exposure: The NCB report specifically identifies that Manipur, Mizoram and Nagaland face the highest exposure due to increased drug production in Myanmar.
    3. Mizoram’s seizure data: Mizoram seized 1,477 kg of amphetamine-type stimulants (ATS) in 2025 out of the national total of 3,485 kg.
    4. Manipur’s seizure data: Manipur accounted for 535 kg in recoveries from other reported states. Delhi (454 kg), Gujarat (308 kg), and Karnataka (164 kg) reported significant quantities, demonstrating that narcotics originating from the northeast are penetrating deep into the hinterland.
    5. Distribution geography: Drugs move through the Barak Valley to Punjab, Gujarat and Maharashtra, making the Northeast a distribution node rather than a consumption centre.

    What does the drone-based trafficking data reveal about the operational maturity of trafficking networks?

    1. Five-fold increase from Pakistan border: Drone-based drug trafficking from across the Pakistan border into India has increased five-fold over the past five years, particularly in Punjab, demonstrating aerial circumvention of border controls.
    2. Incident trajectory (NCB data): Drone trafficking incidents surged from 3 in 2021 to 35 in 2022, 28 in 2023, 178 in 2024, and 305 in 2025, This is a 100-fold increase in incident count over five years.
    3. Seizure volume in 2025: In 2025, drone-related cases resulted in the seizure of 468 kg of narcotics, a 96% increase in quantity over 2024. Punjab recorded 298 cases and 461 kg seized.
    4. UAV sophistication: Trafficking networks are using unmanned aerial vehicles (UAVs) to circumvent traditional border controls, the NCB stated.
    5. Additional reporting states: Geographical spread: Rajasthan and Jammu & Kashmir also reported drone-related trafficking incidents.

    Where does the structural vulnerability in India’s border architecture lie and why cannot existing mechanisms address it?

    1. The FMR design conflict: The FMR facilitates movement of border communities. This objective conflicts with effective narcotics interdiction.
    2. Unfenced stretches: Drugs are smuggled through unfenced and porous stretches of the border.
    3. Geographic chokepoint: National Highway No. 102 through the Manipur corridor, the Champhai route in Mizoram carry both legal trade and illicit narcotics, making interception difficult.
    4. Ethnic armed group control: The poly-drug production in Myanmar is primarily concentrated in areas controlled by ethnic armed groups in Shan State. These groups operate outside the reach of both the Myanmar state and Indian border enforcement, making source-side interdiction impossible.
    5. South Asian arm of Afghan trade: The NCB specifically identifies that the South Asian arm of the Afghan drug trade flows through Pakistan into India via both the land frontier (Punjab, Rajasthan) and the maritime frontier (Gujarat, Maharashtra coastlines).

    Conclusion

    Myanmar’s rise as the world’s alternative opium supplier has created a structural narcotics challenge for India. The Northeast has become an active distribution hub rather than merely a transit corridor. Drone-enabled trafficking further weakens conventional border controls. Addressing the challenge requires technology-driven surveillance, calibrated reforms to the FMR and stronger cooperation with Myanmar.

    PYQ Relevance

    [UPSC 2018] India’s proximity to two of the world’s biggest illicit opium-growing states has enhanced its internal security concerns. Explain the linkages between drug trafficking and other illicit activities such as gunrunning, money laundering, and human trafficking. What countermeasures should be taken to prevent the same?

    Linkage: The PYQ examines the internal security implications of cross-border drug trafficking and its nexus with organised crime. The article explains how Myanmar-origin narcotics trafficking through India’s northeastern border has become a major cross-border security challenge.

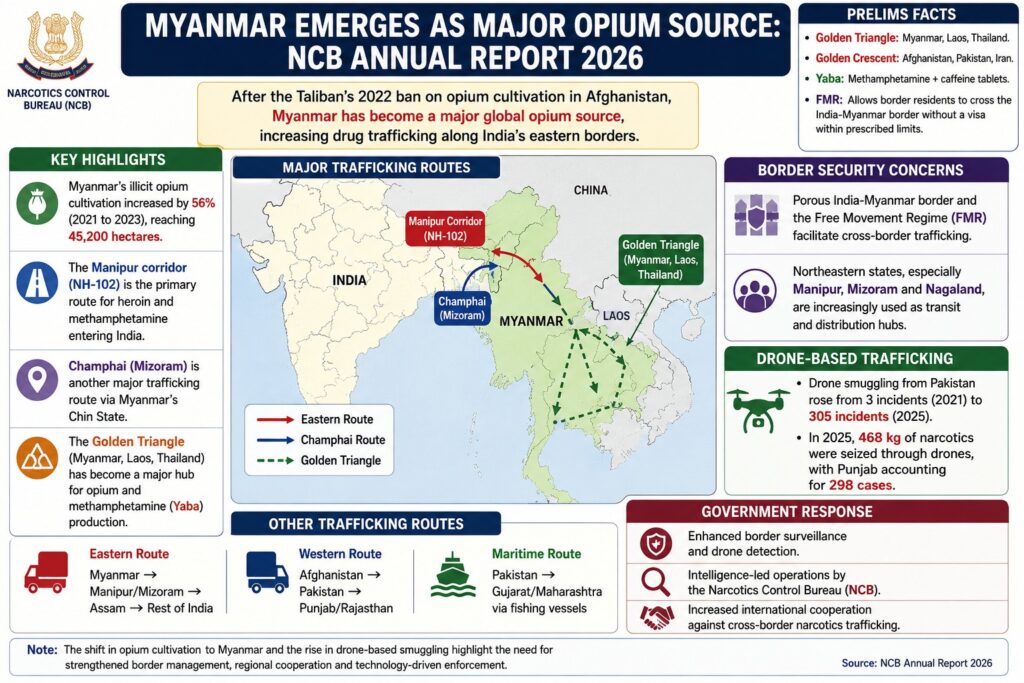
  • Myanmar Replaces Afghanistan as Major Opium Source

    Why in News?

    The NCB Annual Report 2026 states that after the Taliban’s 2022 ban on opium cultivation in Afghanistan, Myanmar has become a major global opium source, increasing drug trafficking along India’s eastern borders.

    Key Highlights

    • Myanmar’s illicit opium cultivation increased by 56% (2021 to 2023), reaching 45,200 hectares.
    • The Manipur corridor (NH-102) is the primary route for heroin and methamphetamine entering India.
    • Champhai (Mizoram) is another major trafficking route via Myanmar’s Chin State.
    • The Golden Triangle (Myanmar, Laos, Thailand) has become a major hub for opium and methamphetamine (Yaba) production.

    Border Security Concerns

    • Porous India-Myanmar border and the Free Movement Regime (FMR) facilitate cross-border trafficking.
    • Northeastern states, especially Manipur, Mizoram and Nagaland, are increasingly used as transit and distribution hubs.

    Drone-Based Trafficking

    • Drone smuggling from Pakistan rose from 3 incidents (2021) to 305 incidents (2025).
    • In 2025, 468 kg of narcotics were seized through drones, with Punjab accounting for 298 cases.

    Other Trafficking Routes

    • Eastern Route: Myanmar → Manipur/Mizoram → Assam → Rest of India.
    • Western Route: Afghanistan → Pakistan → Punjab/Rajasthan.
    • Maritime Route: Pakistan → Gujarat/Maharashtra via fishing vessels.

    Government Response

    • Enhanced border surveillance and drone detection.
    • Intelligence-led operations by the Narcotics Control Bureau (NCB).
    • Increased international cooperation against cross-border narcotics trafficking.

    Prelims Facts

    • Golden Triangle: Myanmar, Laos, Thailand.
    • Golden Crescent: Afghanistan, Pakistan, Iran.
    • Yaba: Methamphetamine + caffeine tablets.
    • FMR: Allows border residents to cross the India-Myanmar border without a visa within prescribed limits.